Executive coaching · Fractional advisory
You chose your security leader. I help them become the one you need.
I work alongside CISOs and security leaders as a trusted adviser and coach — contributing hands-on where it counts, and helping them round out into the leader their role and organisation demand.
Operating experience across resources, financial services, aviation, energy, health, retail and government.
Who I work with
Three different seats. One question: is our security leader equipped for what we're asking of them?
Boards & directors
“Is our CISO ready for the questions we need to ask?”
Independent perspective from someone who has written the board paper and faced the questions — and a trusted adviser working alongside your CISO so the board gets the leader it needs.
CEOs, CIOs & IT leadership
“We've backed our security leader. How do we help them step up?”
Sponsor a senior adviser and coach for your CISO or security lead: practical, fractional contribution on the work in front of them now, and development that stays with them.
CISOs & security leaders
“I can do this job. I want to do it at the level it now demands.”
A confidential adviser and coach who has held the seat — someone to think out loud with, test the big calls against, and help you grow into the leader the role demands.
How I work
I don't replace your security leader. I walk alongside them.
Some engagements begin with fractional advisory and grow into coaching as trust builds. Others start with coaching. Either way, the leader you chose stays in the seat.
-
01
Contribute
I bring the experience to the table.
As a fractional adviser, a few days a month in the room: a sounding board on material risk calls, a second pair of eyes on the board paper, hands-on help where the program is stuck. Your leader stays in charge.
-
02
Develop
I help them grow into the role.
Coaching that works on the real job as it happens — judgement under load, presence in the boardroom, leading their own team, and a pace they can sustain.
-
03
Fit
Shaped to your organisation.
A regulator-facing bank, an OT-heavy resources company and a government agency each ask something different of their security leader. We work on the leader this role needs — not a generic template.
Ways to work together
A trusted adviser in the room. A coach in their corner.
Contribute
Fractional advisory
Senior security leadership input, a few days a month, alongside your CISO. A sounding board for the big calls, a sharper board narrative, and practical help where the program needs it.
- Sounding board
- Board papers
- Program reviews
Contribute
Board & executive advisory
Independent counsel for directors and executives: an honest read on how security leadership is tracking, the narrative and metrics that hold under sharp questions, and a second opinion when it matters.
- Board-readiness
- Risk narrative
- Independent perspective
Develop
Executive coaching
Confidential 1:1 coaching for sitting and newly appointed CISOs. Decision load, board scrutiny and a sustainable operating rhythm — with a trained coach who has done the job.
- New CISOs
- Sitting CISOs
- Employer-sponsored
Develop
Leadership bench development
Developing the managers beneath the CISO, so the function multiplies rather than sending every decision back upstairs.
- Security managers
- Delegation
- Security culture
I work with a small number of organisations at a time, so every engagement gets real attention. Each is scoped to an outcome and timeframe — typically 8–16 weeks — with pricing on application.
Track record
I don't advise from the sidelines. I've Delivered.
ISO 27001, in place
Led the governance, risk and compliance work for an ISO 27001 project, so the organisation had a management system it could run.
A SOC, stood up
Established the SOC, SIEM and critical incident response design for a major Western Australian energy utility.
The first board paper
Rebuilt a large retailer's security function and wrote its first quarterly board report to an ASX-listed parent.
A state program
Led program management of a large-scale security capability for a cluster of state government agencies.
These describe work I have led. They are not a list of current clients.
Why it matters
When the security leader burns out, the program leaves with them.
Losing a CISO is a business risk, not a personal setback. Each departure resets relationships with the board, regulators and the team, and stalls the change agenda. The pressures behind it aren't technical — they're leadership pressures, and a well-supported leader can carry them.
Decision load
The last stop on every material risk call. Judgement under load: what to decide, defer, or refuse to carry alone.
Board scrutiny
Directors want risk, investment and residual exposure — not a tour of the toolset.
Sustainable pace
An operating rhythm with recovery built in, so the leader is still there to finish what they started.
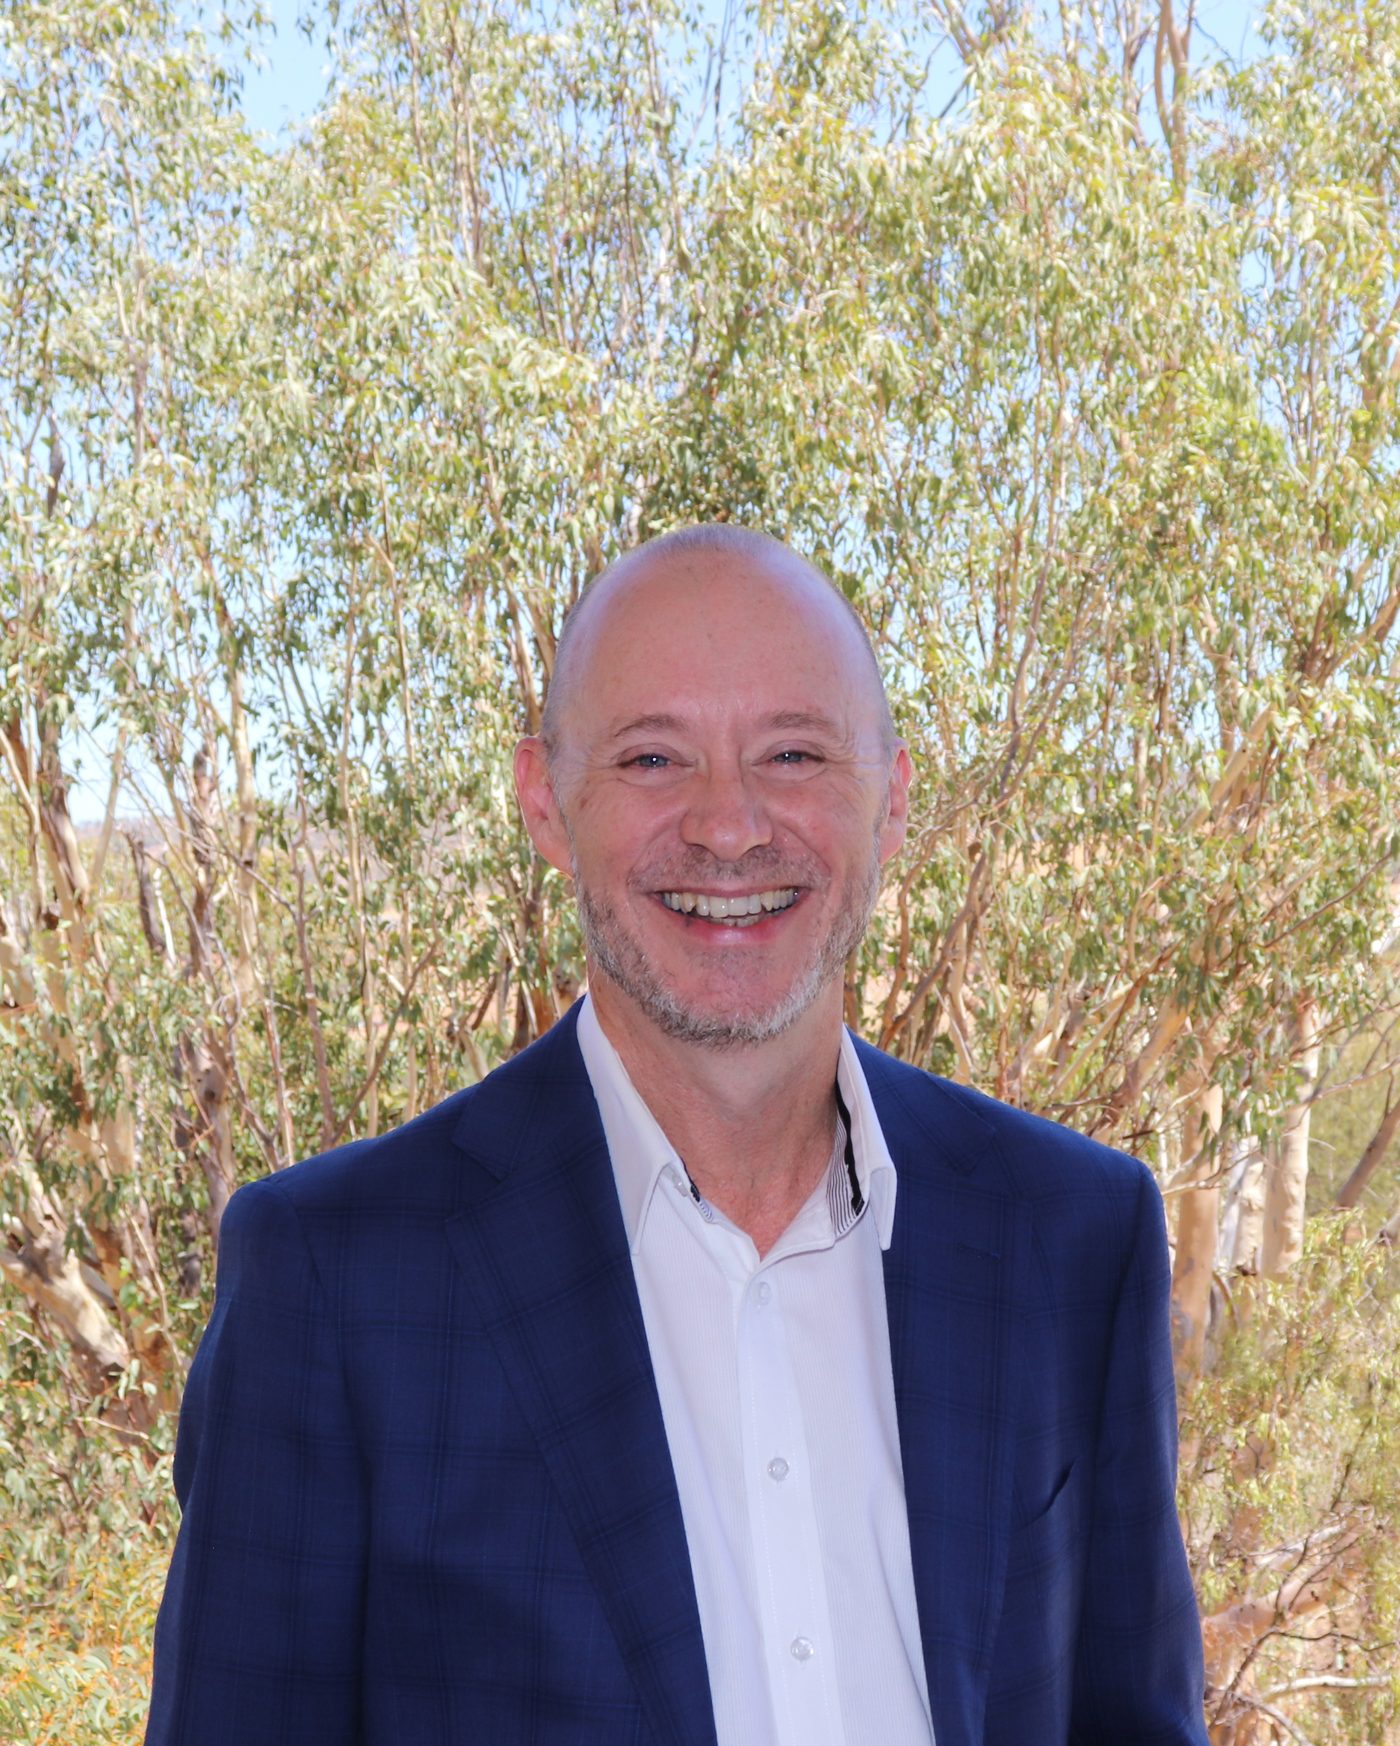
Campbell Carew
20 Years of Experience. Now in your leader's corner.
I spent more than two decades building and leading security functions in organisations that can't treat cyber as a side project. Along the way I watched capable leaders walk away from roles they were good at — not for lack of a framework, but because the load was never managed. Now I work alongside security leaders — contributing what two decades in the seat taught me, and helping them become the leader their organisation needs.
- CISSP
- MBL, Curtin University
- Cert IV Mentoring & Coaching
- ICF member
- Sessional academic, Murdoch University
Let's talk about the leader your organisation needs.
One conversation is usually enough to know whether fractional advisory, coaching or both is the right fit. I take on a small number of engagements at a time.